Know what is working, what is changing and where to act.
Sentinet³ continuously checks the availability and performance of systems, network, applications and physical environments, and with the Infinity modules brings traffic, host security, vulnerabilities and cyber risk into the same console.
- A single web console, from the big picture down to the individual service
- IT and the physical data center environment in the same model
- Physical or virtual appliances, with data always inside your perimeter
Check, Alert, Act, Analyse
A continuous cycle covering IT monitoring (systems, network, applications), data center monitoring with Disaster Prevention, and OT monitoring compatible with Modbus, Fieldbus, OPC and SCADA.
Check
Continuously verifies the availability and performance of hosts, devices, applications, services and environmental sensors.
Alert
Notifies anomalies to the right people by email, SMS and voice, with on-call groups and escalation.
Act
Launches preconfigured automatic corrective actions before the problem turns into a service outage.
Analyse
Event correlation and Root Cause Analysis, Time Machine, Situation Analysis and SLA reports.
Leader in IT monitoring
Since 2016 Sentinet³ has been included in the Gartner Market Guide for IT Monitoring Tools, the only Italian system. Developed, maintained and supported by Fata Informatica since 2004, it is adopted by strategic customers in Defence, Central Public Administration and Energy. The company
A common foundation, modules that extend it
The Core collects the states, relationships and history of the infrastructure. The Infinity modules reuse the same context to answer network and security questions. Adoption can be gradual, in the same console.
Proactive infrastructure monitoring
Continuous checks on hosts, devices, applications, services and environmental sensors, with thresholds, notifications, escalation, automation and historical analysis.
- Systems and virtualisation
- Network
- Applications
- Data center
- Time Machine
- SLA
Cybersecurity Intelligence
Who communicates with whom, what is exposed, which vulnerabilities really matter and which attack paths threaten critical assets.
- Network Insight
- Security Insight
- Threat Insight
- AI Insight
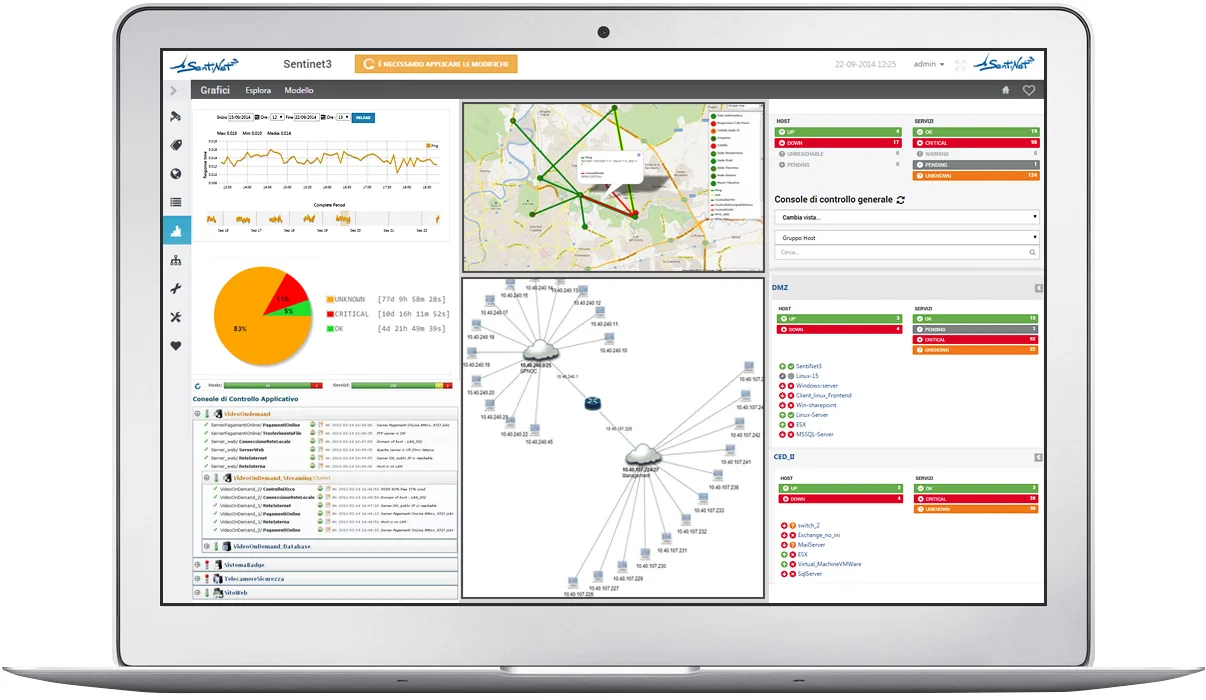
From the single host to the big picture
A host that is up does not guarantee that its services are usable. The Core assigns specialised checks to each node, each with its own frequency, thresholds, state and history.
Infrastructure and systems
Windows, Linux, Unix, hardware, RAID and storage, VMware, Hyper-V, Xen and KVM, and essential services such as DNS, DHCP and Active Directory.
Network
Routers, switches and firewalls: reachability, ports, bandwidth, latency and errors, with Interface Inspector and SNMP traps.
Applications and services
Application servers, Microsoft services and databases, HTTP checks and web transactions linked to the resources that support them.
Environment and data center
Temperature, humidity, power and UPS, smoke and flooding, access and video surveillance, with automatic corrective actions.
Console and maps
Enterprise Console, Tactical Overview and multi-level maps from the geographic site down to the rack, also on mobile.
Alerts and automation
Notifications by email, SMS and voice, on-call groups, escalation, anti-flooding and preconfigured corrective actions.
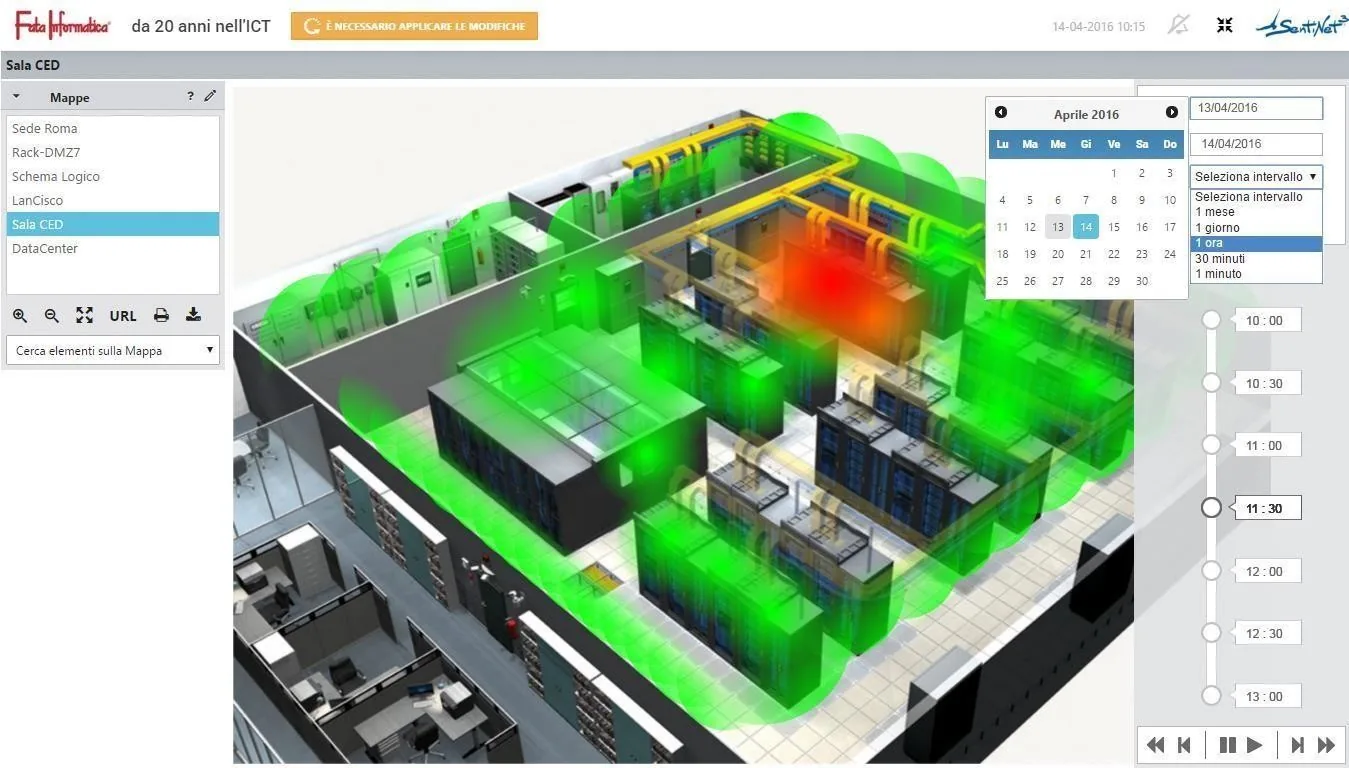
Time Machine: the fault in the context in which it occurred
Takes the console and maps back to the date and time of interest and reconstructs, in a synchronised way, the state of systems and services at that moment. Ideal when an incident happens at night and has to be understood the next morning.
- Start from the moment indicated by the notification or the log
- See the hosts and services that were critical at that moment together
- Compare states before and after the anomaly
From the alert to verifying the recovery
Five typical situations and how the Core helps to prevent, diagnose and close them.
Gradual saturation of a service
The mail server disk fills up steadily. Thresholds, notification to the owners and an authorised mitigation procedure before the outage.
Multi-site connectivity failure
Several services at one site go down together. Topology, interfaces and maps distinguish the failure of a shared device from that of individual systems.
Abnormal temperature in the equipment room
The environmental map locates the hot spot, the alarm reaches the technicians and an automation starts the auxiliary cooling.
Anomaly during the night
Time Machine reconstructs the state at the time of the fault, Situation Analysis shows the most critical objects and the SLA history quantifies the interruption.
A new service to bring under control
Autodiscovery finds hosts and ports, a Pattern configures the checks and the device enters maps and reports.
And on the security side?
With Infinity: anomalous traffic, host attack surface, priority vulnerabilities and attack paths towards critical assets.
From observability to knowledge of risk
Specialised modules that correlate infrastructure, traffic, hosts, vulnerabilities and alarms to decide where to act first.
Network Insight
NetFlow, sFlow and IPFIX flows: top talkers, relationships between hosts, period comparison and flow checks.
Learn moreApplication Insight
OpenTelemetry-based APM, End User Experience and Business Monitoring.
Learn moreSecurity Insight
Attack surface, logins, processes and software of the hosts, with SIEM alarms on the maps.
Learn moreThreat Insight
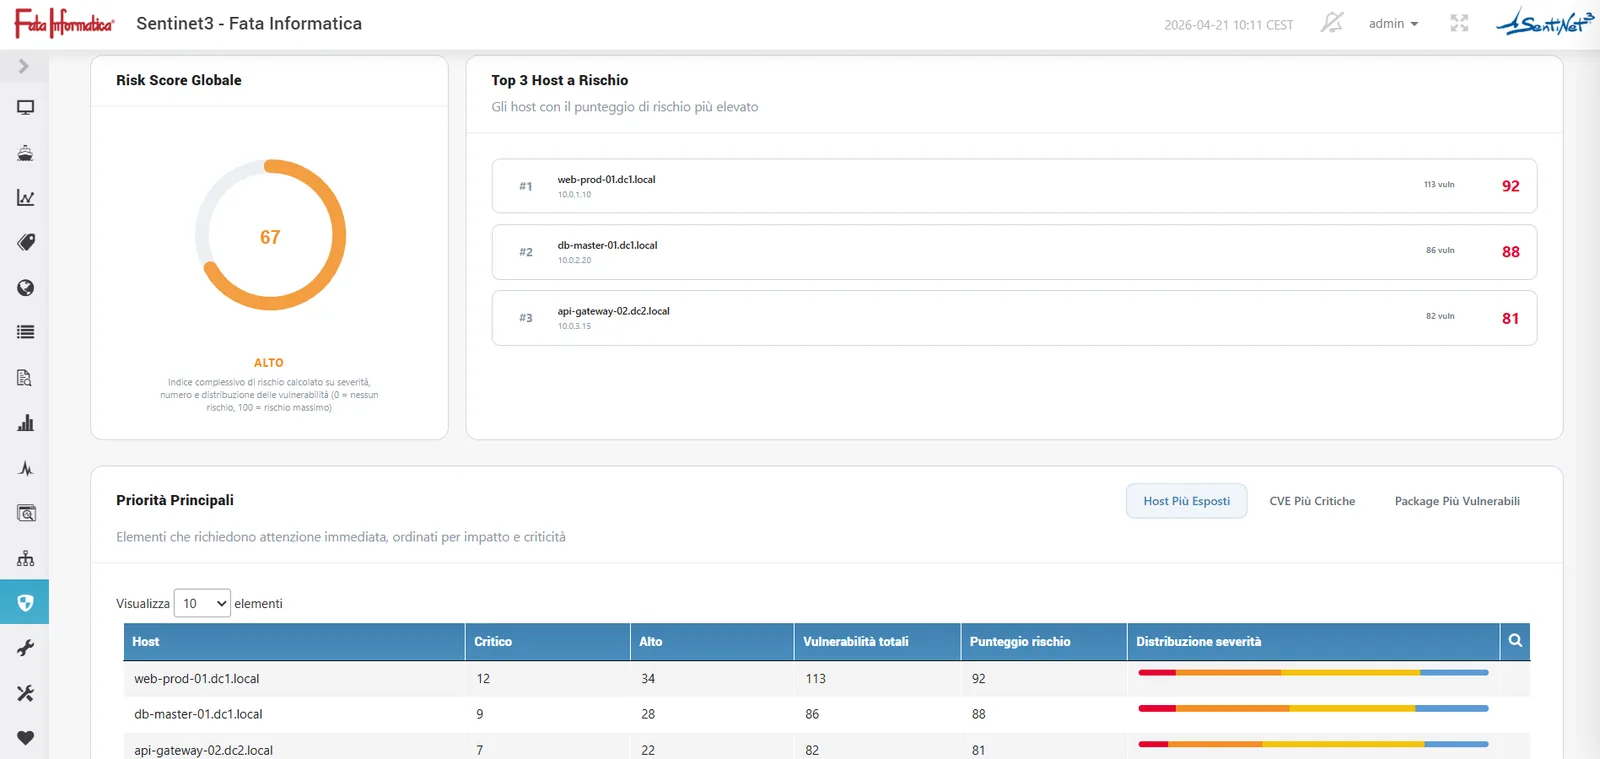
Continuous Vulnerability Assessment, attack paths, chokepoints and risk indicators.
Learn moreAI Insight
Natural language questions and agentic AI running on-premise, inside the customer’s perimeter.
Learn more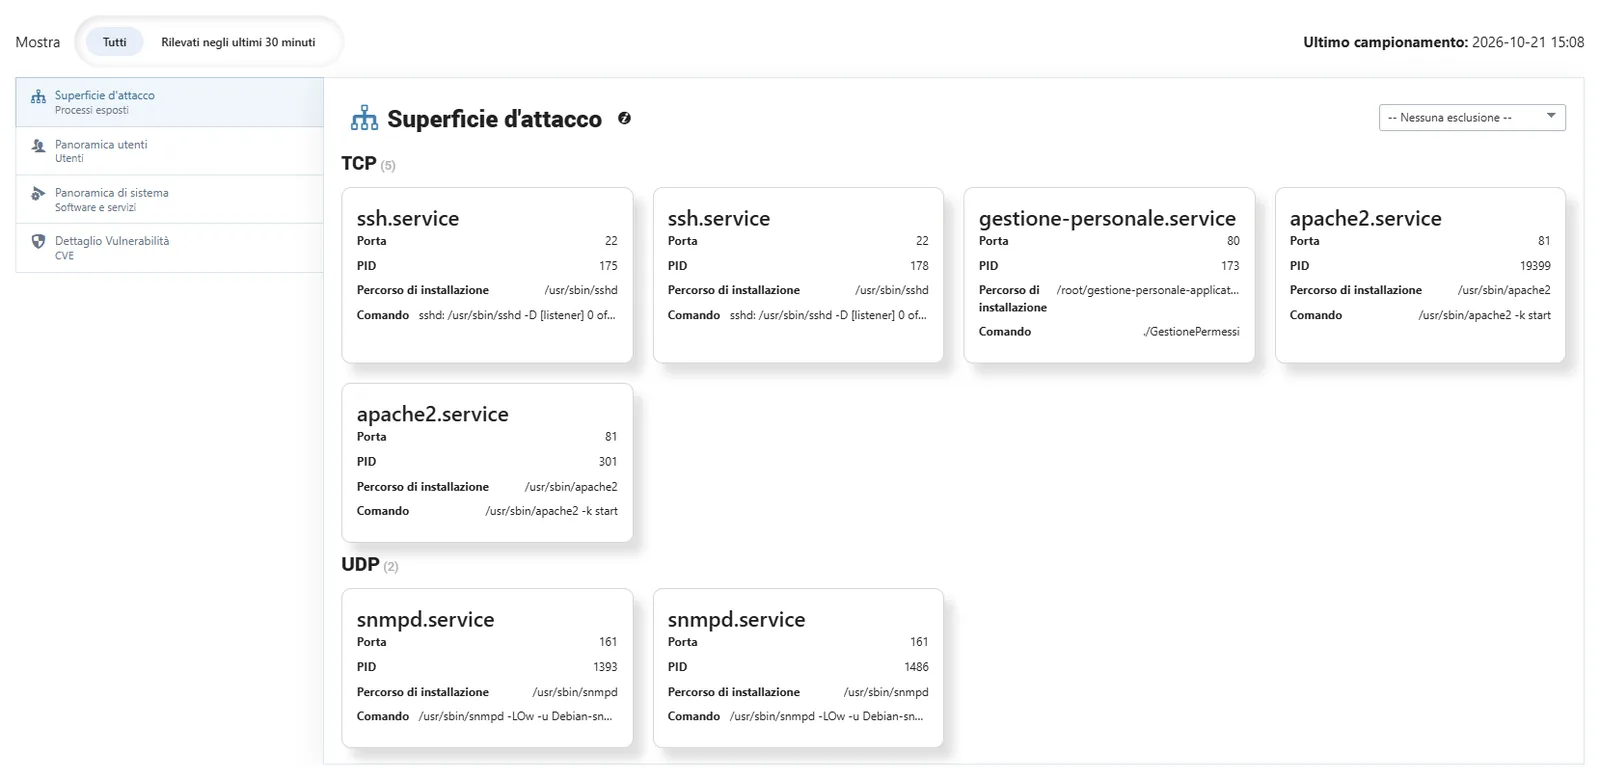
Want to see Sentinet³ on your infrastructure?
Tell us about your environment: sites, technologies, critical services. We will show you how Core and Infinity can work on your case.