Use scenarios
From the alert to confirmed recovery: real situations where Sentinet³ Core and the Infinity modules make the difference.
Prevention, diagnosis and recovery
Five scenarios that show Core at work, with the functions involved in each.
Progressive saturation of a service
A mail service keeps responding, but the free disk space steadily decreases. Core detects when thresholds are exceeded, alerts those responsible and can trigger a pre-authorised automated mitigation procedure. History and charts help establish the urgency and prevent the outage.
See: Infrastructure and systems, Alerts and automation, SLA and reports
Multi-site connectivity failure
Several services at one site become unavailable in the same time window. The topology view, interface checks and geo-referenced maps help distinguish the failure of a shared device from the unavailability of individual systems. Escalation routes the event to the team responsible for connectivity.
See: Discovery and topology, Network, Console and maps, Alerts and automation
Abnormal temperature in the equipment room
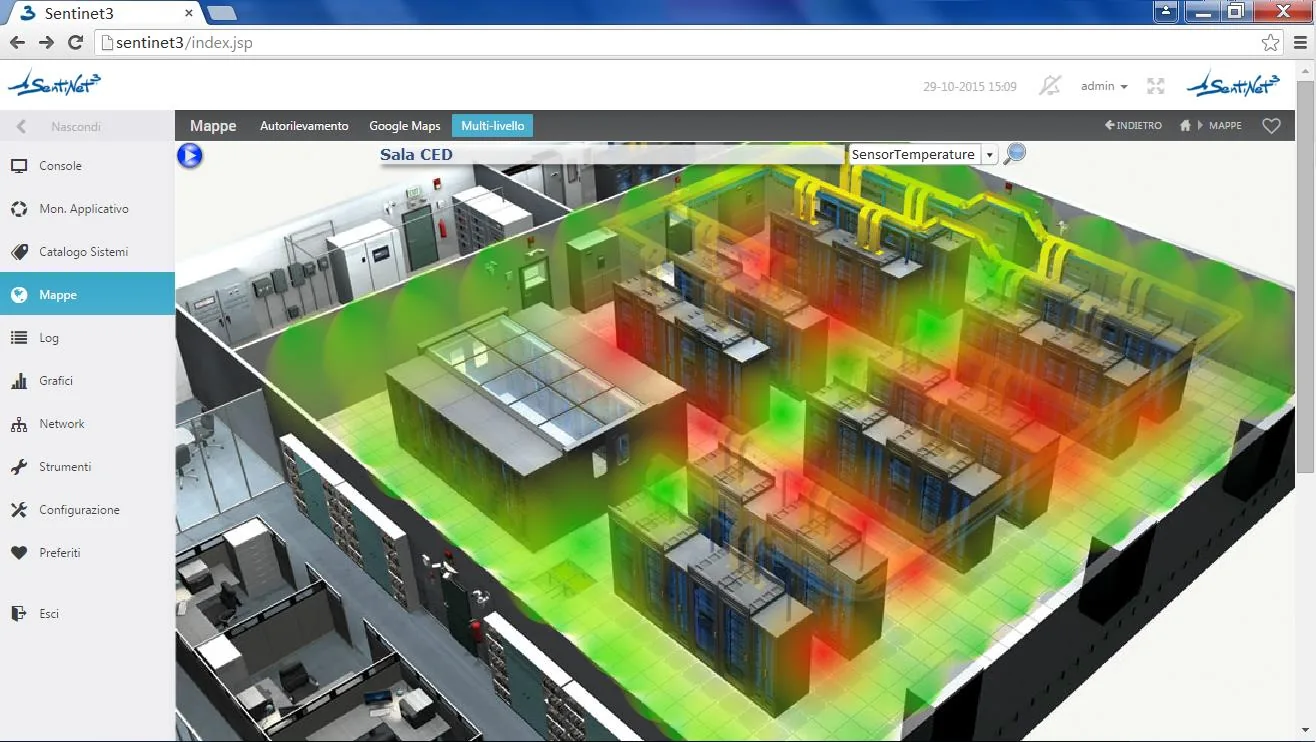
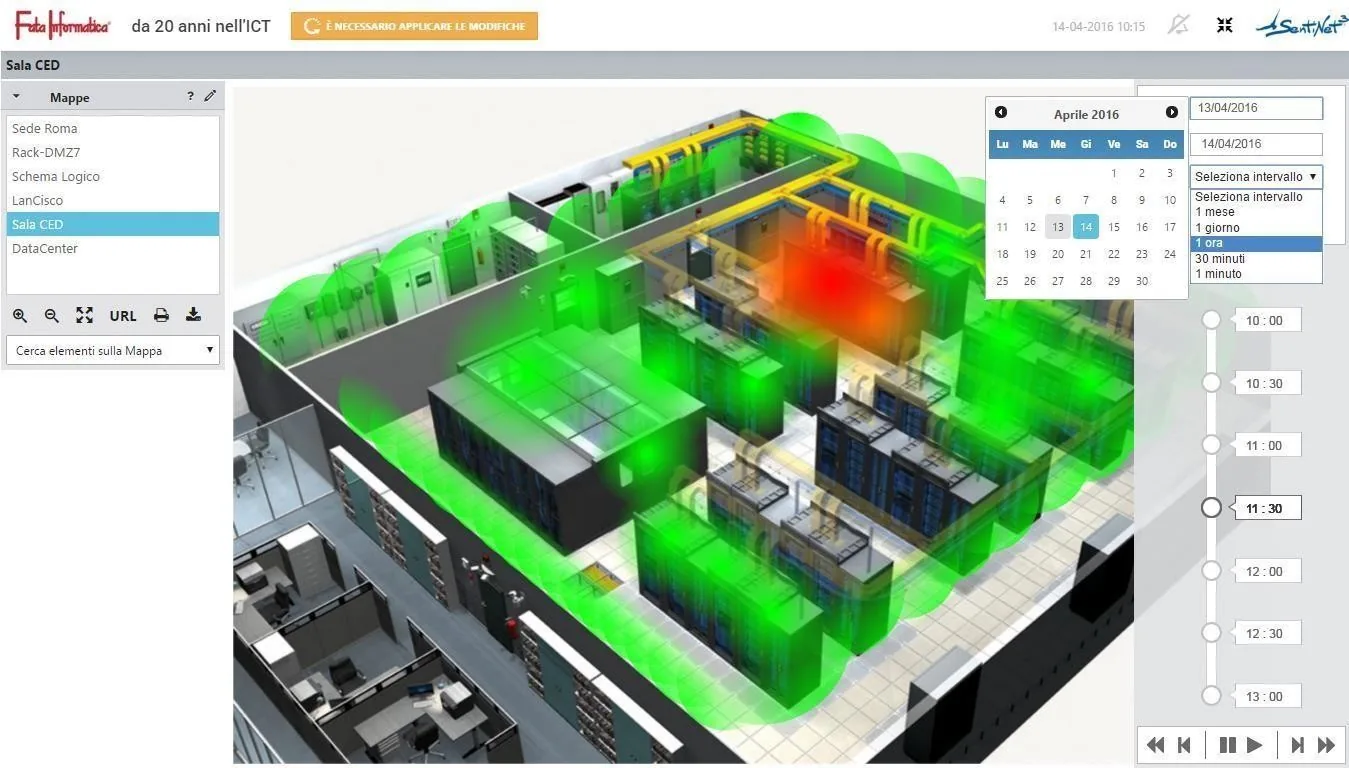
A sensor detects a rapid rise in temperature in a data centre aisle. The environmental map locates the hot spot, the alert reaches the technical staff and an automation can start an auxiliary cooling unit. Historical charts confirm that values have returned within the defined range.
See: Environment and data centre, Console and maps, Alerts and automation
An anomaly that occurred overnight
A sequence of events affects several hosts and services while the operations centre is unattended. The technician uses Time Machine to reconstruct the state of the components at the time of the fault; Situation Analysis highlights frequently critical objects and the SLA history quantifies the outage.
A new service to bring under control
Autodiscovery detects a host and its available ports. A Pattern associated with the technology quickly configures the checks, the console includes the new states and the device enters the maps and reports. Less manual work is needed to extend the scope of control.
See: How it works (patterns and templates), Discovery and topology, Console and maps
The common thread
The value of Core lies in the continuity between observation, context, analysis and action: not isolated measurements, but an operational platform that guides operators from the alert to confirmed recovery.
Network and security operational scenarios
With the Infinity modules, the same infrastructure data can be read together with traffic, host status, vulnerabilities and alerts.
| Scenario | How it helps | Module |
|---|---|---|
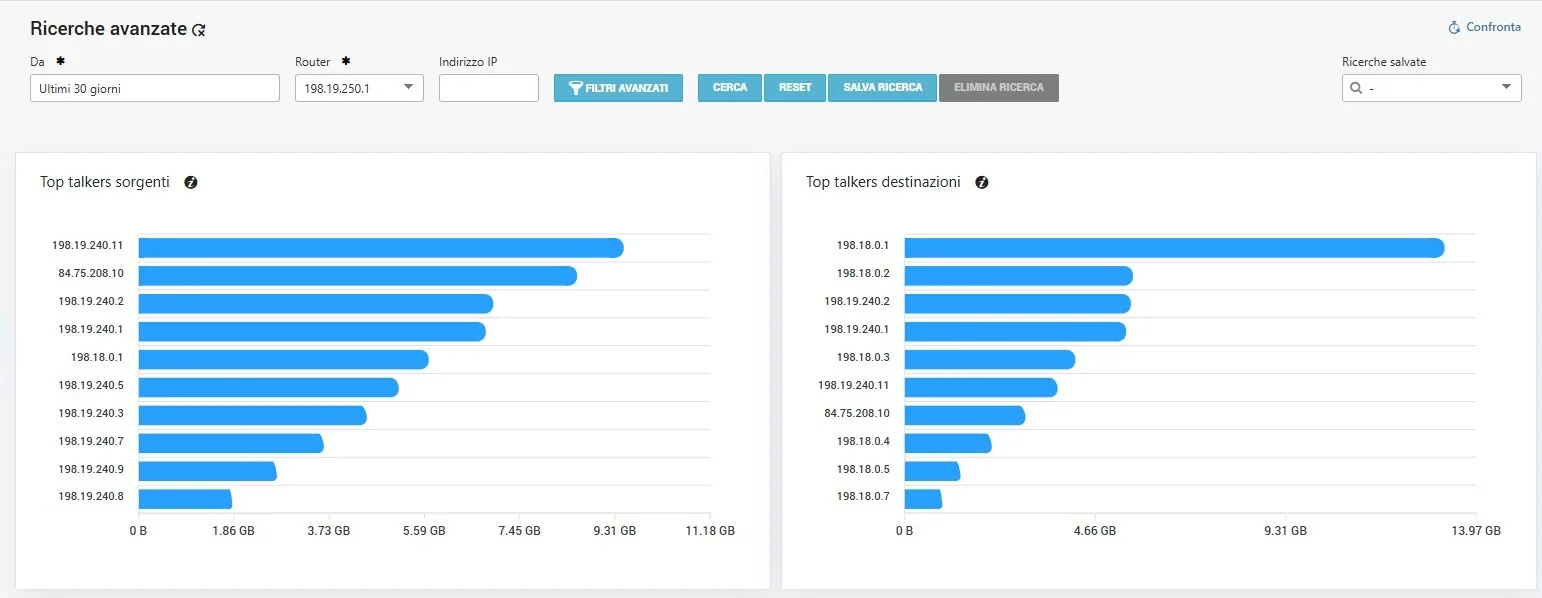
| Saturated link | Isolation of critical periods, responsible hosts, applications and services, and volumes generated. | Network Insight |
| Potentially compromised endpoint | Reconstruction of counterparts, first and last contacts, and new or malicious flows. | Network Insight |
| Inactive backup or replication | Check on the last expected communication between hosts and generation of notifications. | Network Insight |
| Uninventoried device | Identification in the flows and addition of the host to monitoring. | Network Insight |
| Capacity planning | Comparison of volumes and services over time to support infrastructure decisions. | Network Insight |
| Network and policy audits | Reconstruction of communications towards critical systems and checks on disallowed services. | Network Insight |
| Protecting a critical asset | Backtracking of possible paths, identification of chokepoints and hardening priorities. | Threat Insight |
| Investigation and response | Correlated reading of SIEM alerts, host status and contextualised traffic. | Security Insight, Network Insight |
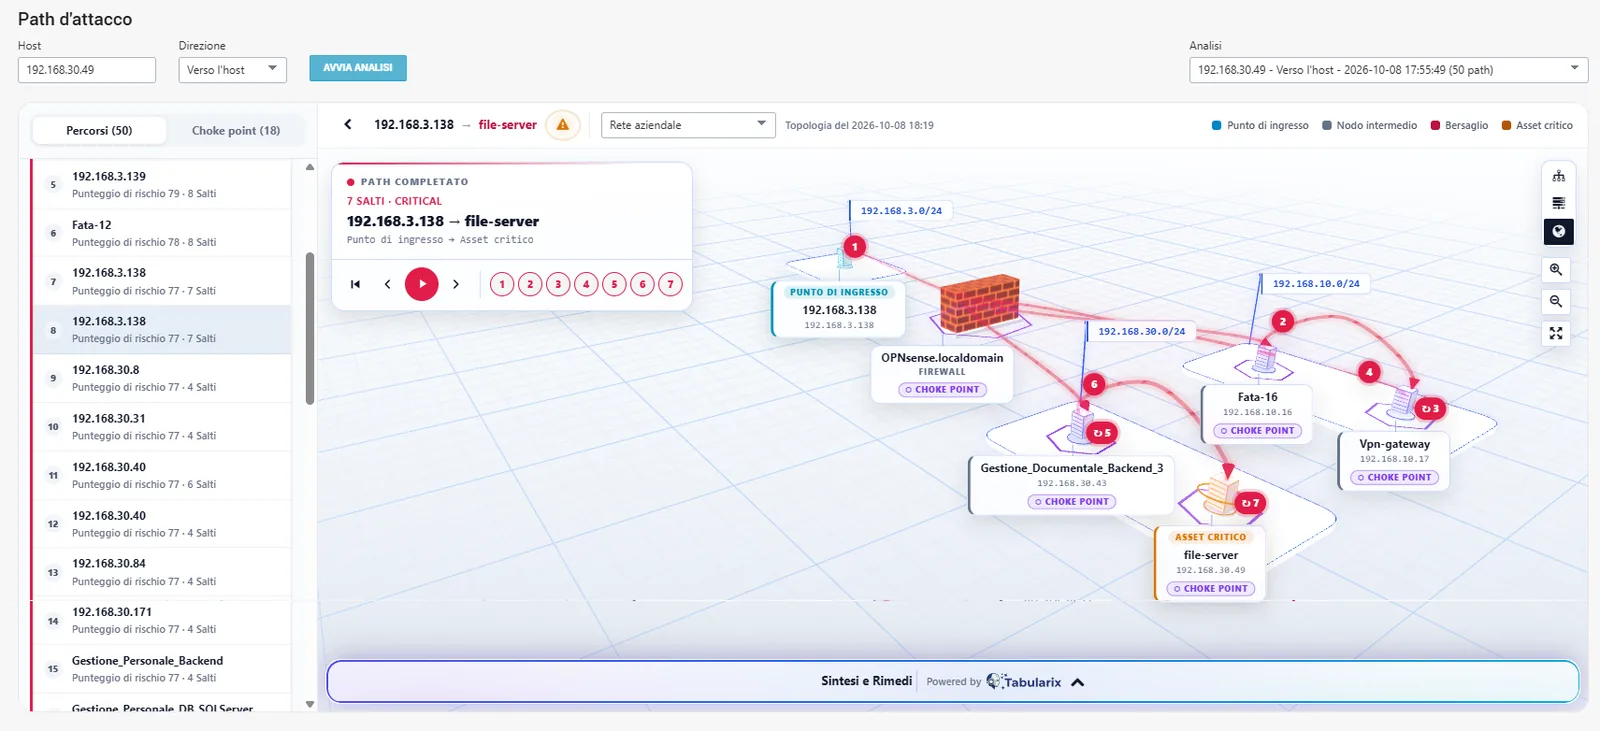
Taken together, these capabilities make it possible to use Sentinet³ Infinity as a Cybersecurity Intelligence layer, including in SOC and Managed Security Services offerings. Integrating the evidence the customer already has reduces information silos and improves the technical and organisational understanding of risks.
Value for different teams
| Audience | Operational contribution |
|---|---|
| SOC and first-level analysts | SIEM alerts on maps, information on systems, possible paths and triage support. |
| Vulnerability Management | Continuous identification of exposures and context-based priorities. |
| CTEM and Cyber Risk | Attack paths, chokepoints and monitoring of risk indicators. |
| Security Operations Automation | Assisted execution of analyses and correlations through agentic AI. |
| Network administrators and NetOps | Top talkers, relationships, historical series, capacity planning and flow alerts. |
| IT Managers and senior management | Unified view, impact assessment, information to support investment and mitigation decisions. |
Related topics
Want to see Sentinet³ on your infrastructure?
Tell us about your environment: sites, technologies, critical services. We will show you how Core and Infinity can work on your case.